AyeWatch for Security Teams, threat-intel and vendor-risk monitoring
Continuously monitor vendor breach announcements, CVE disclosures, vendor status pages, and threat-actor mentions across open sources. Semantic AI cuts down on the noise that breaks traditional CTI feeds.
For security teams
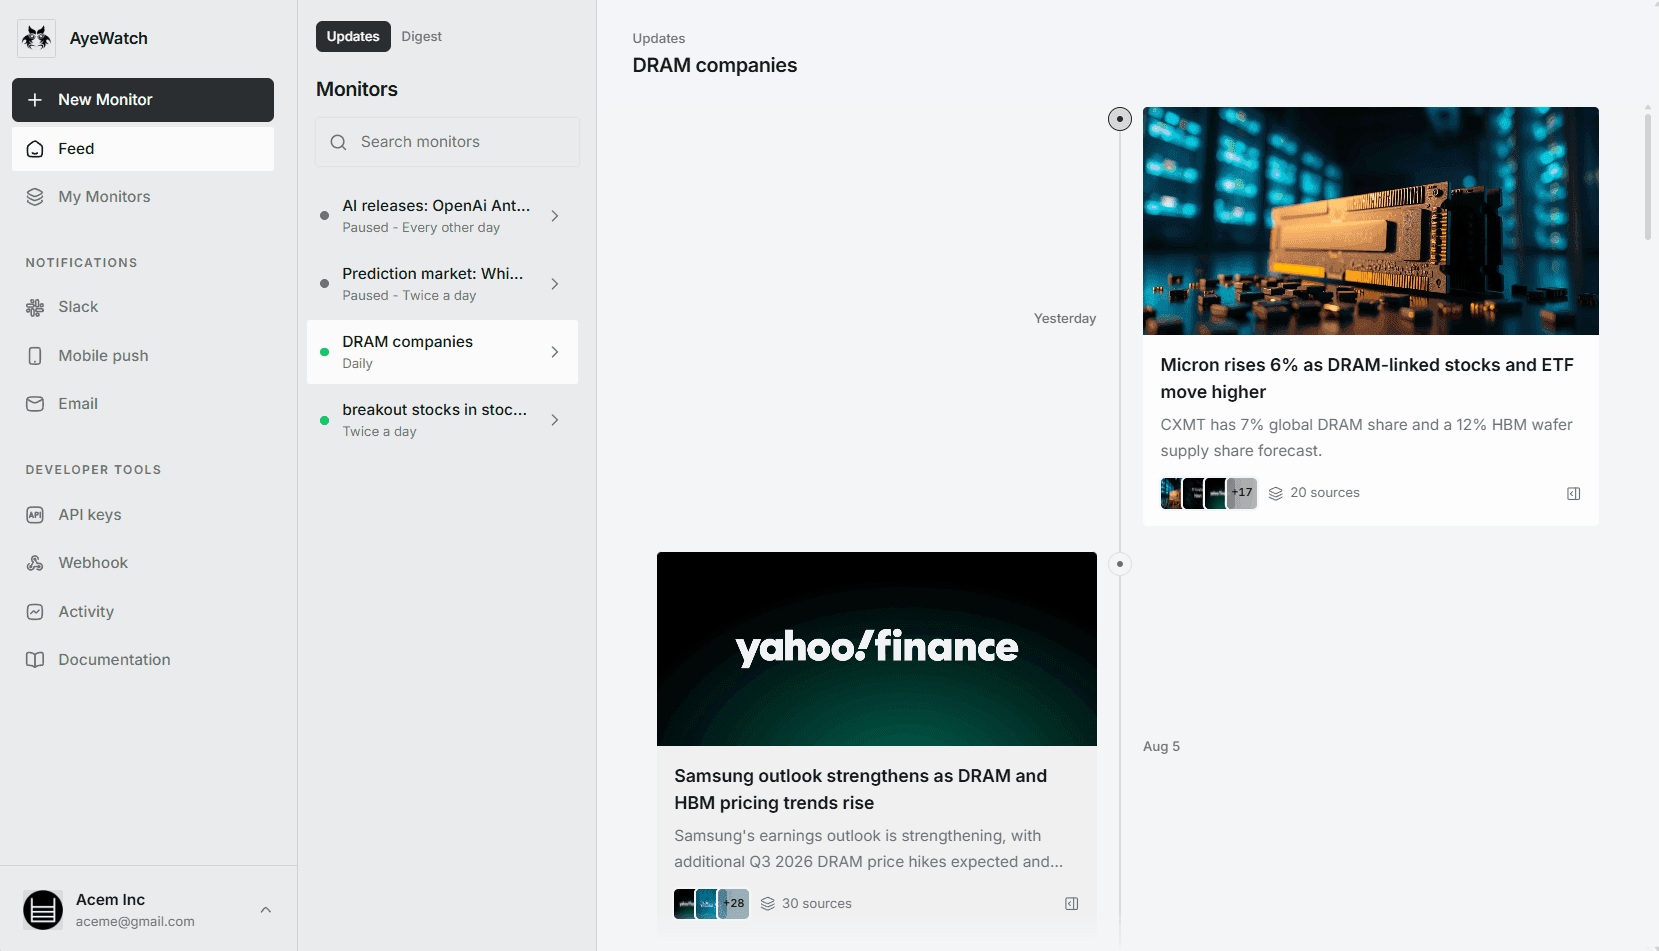
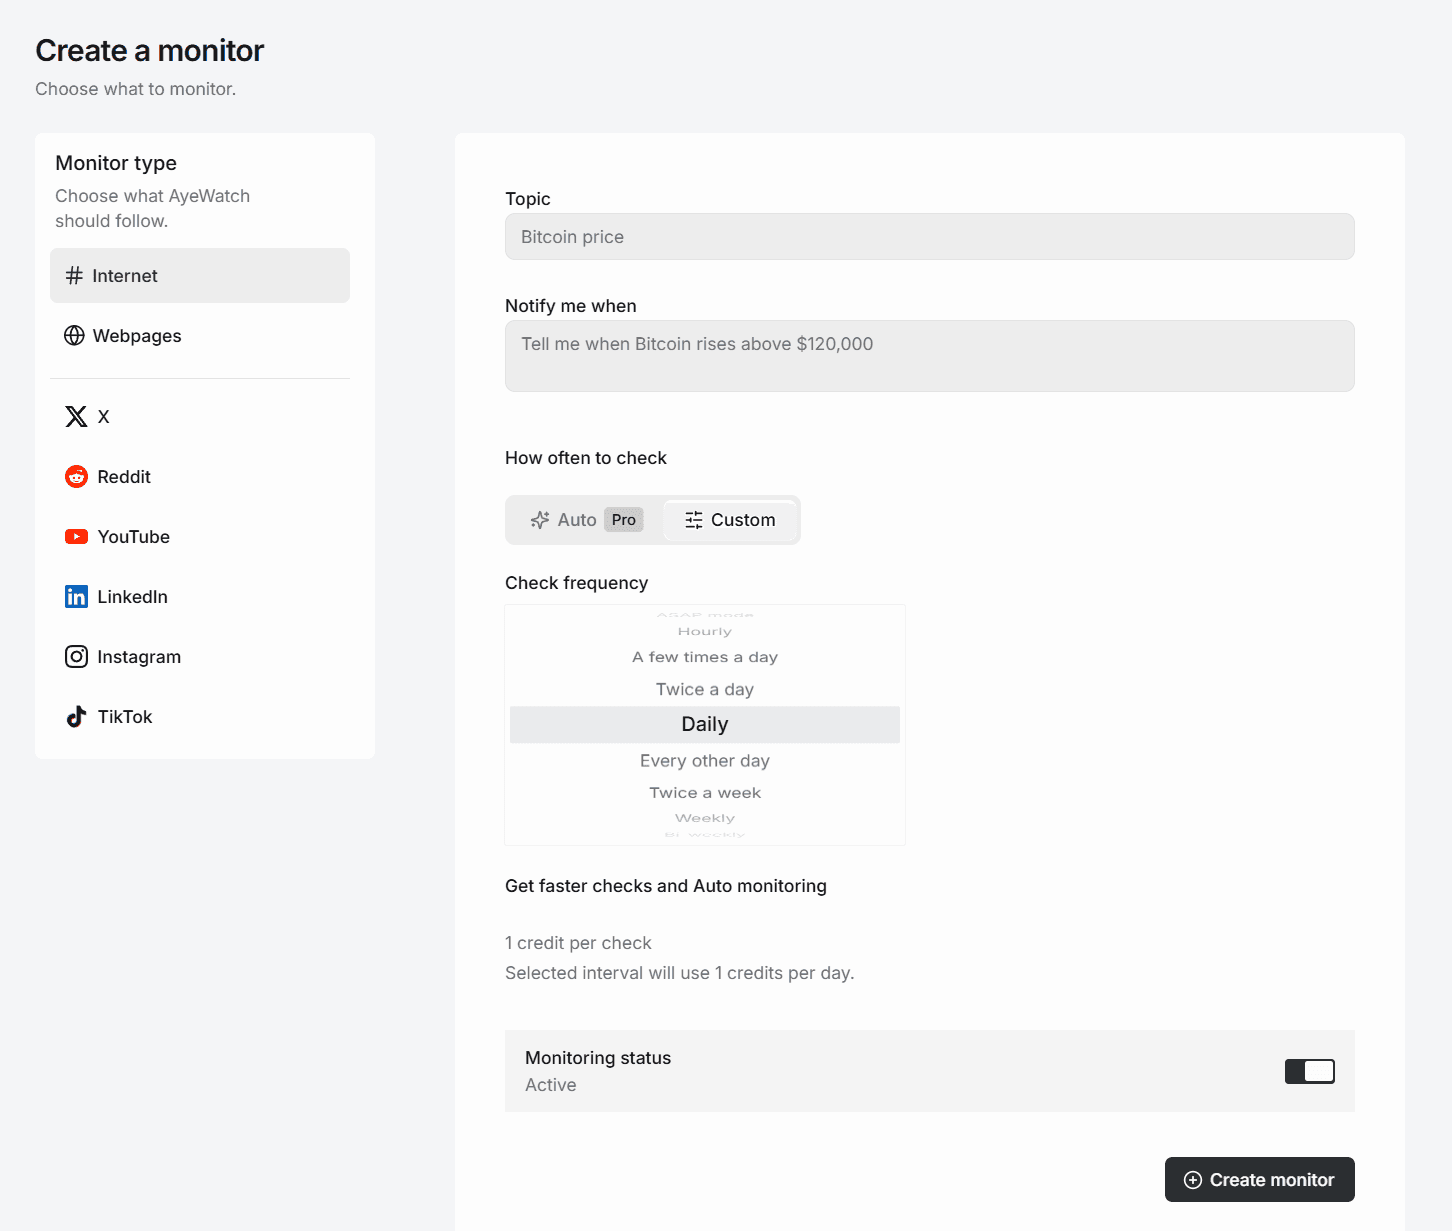
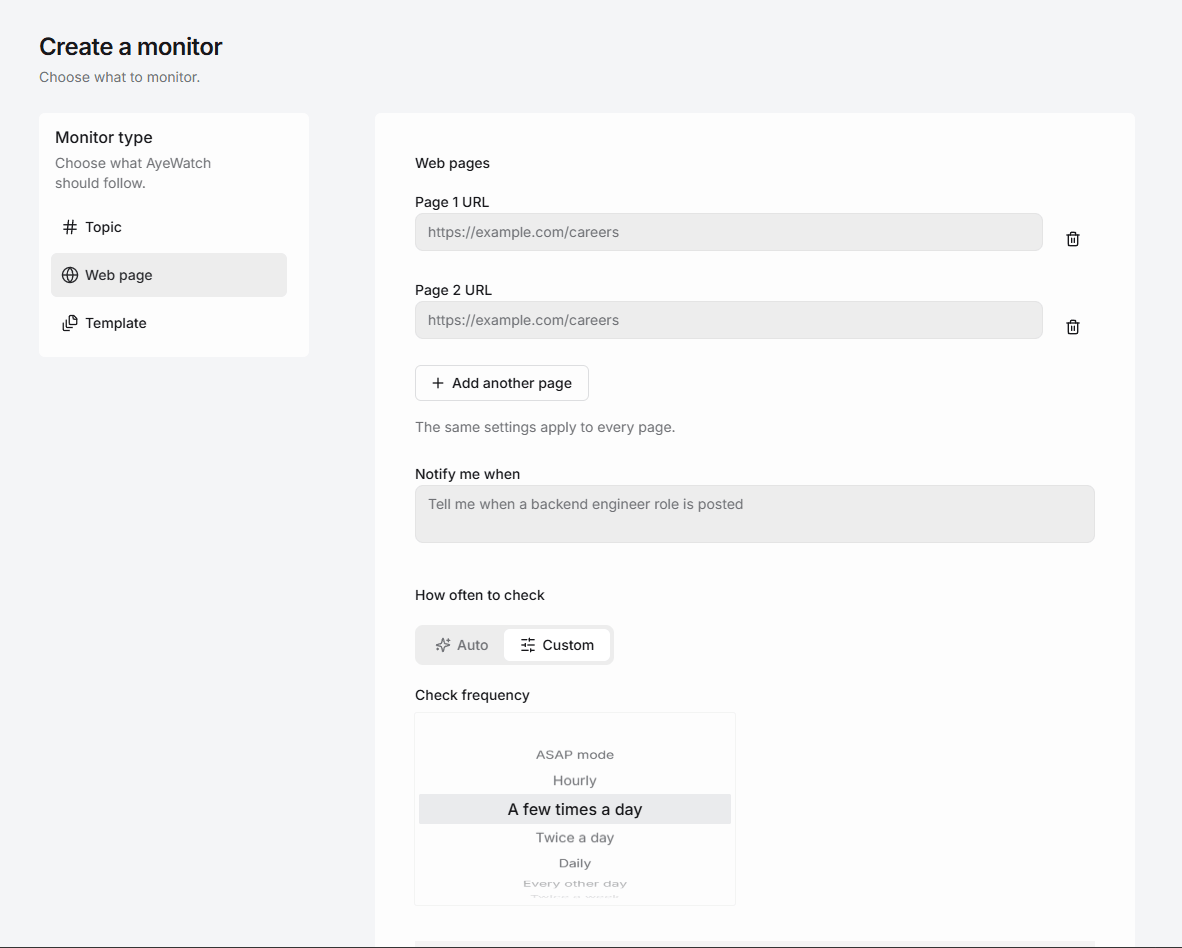
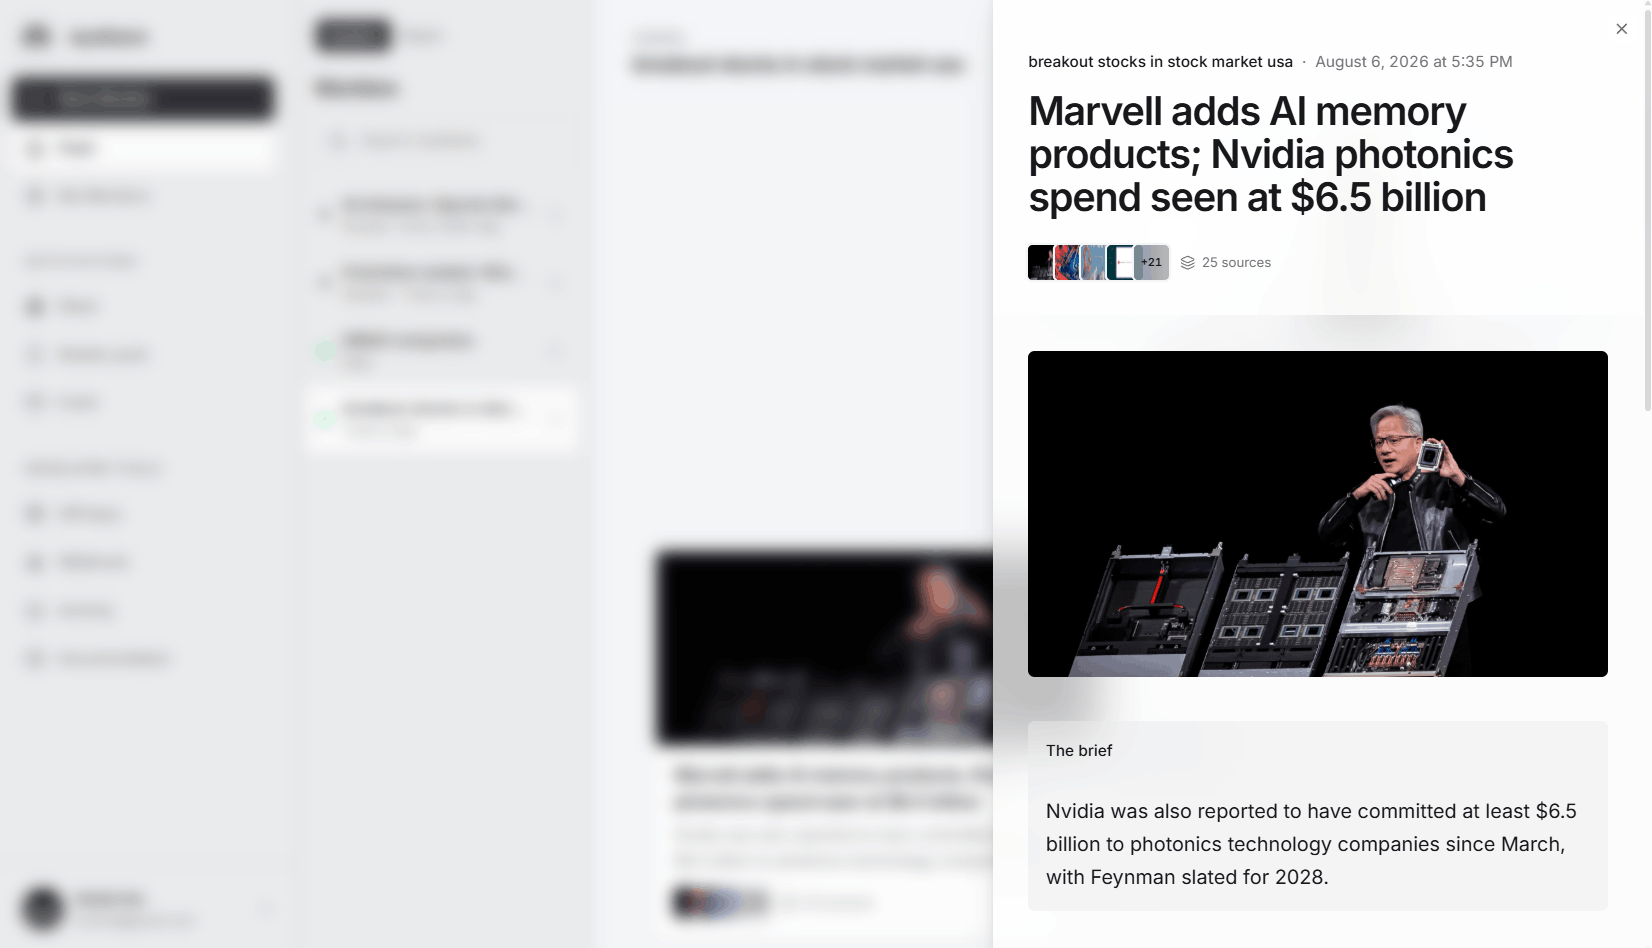
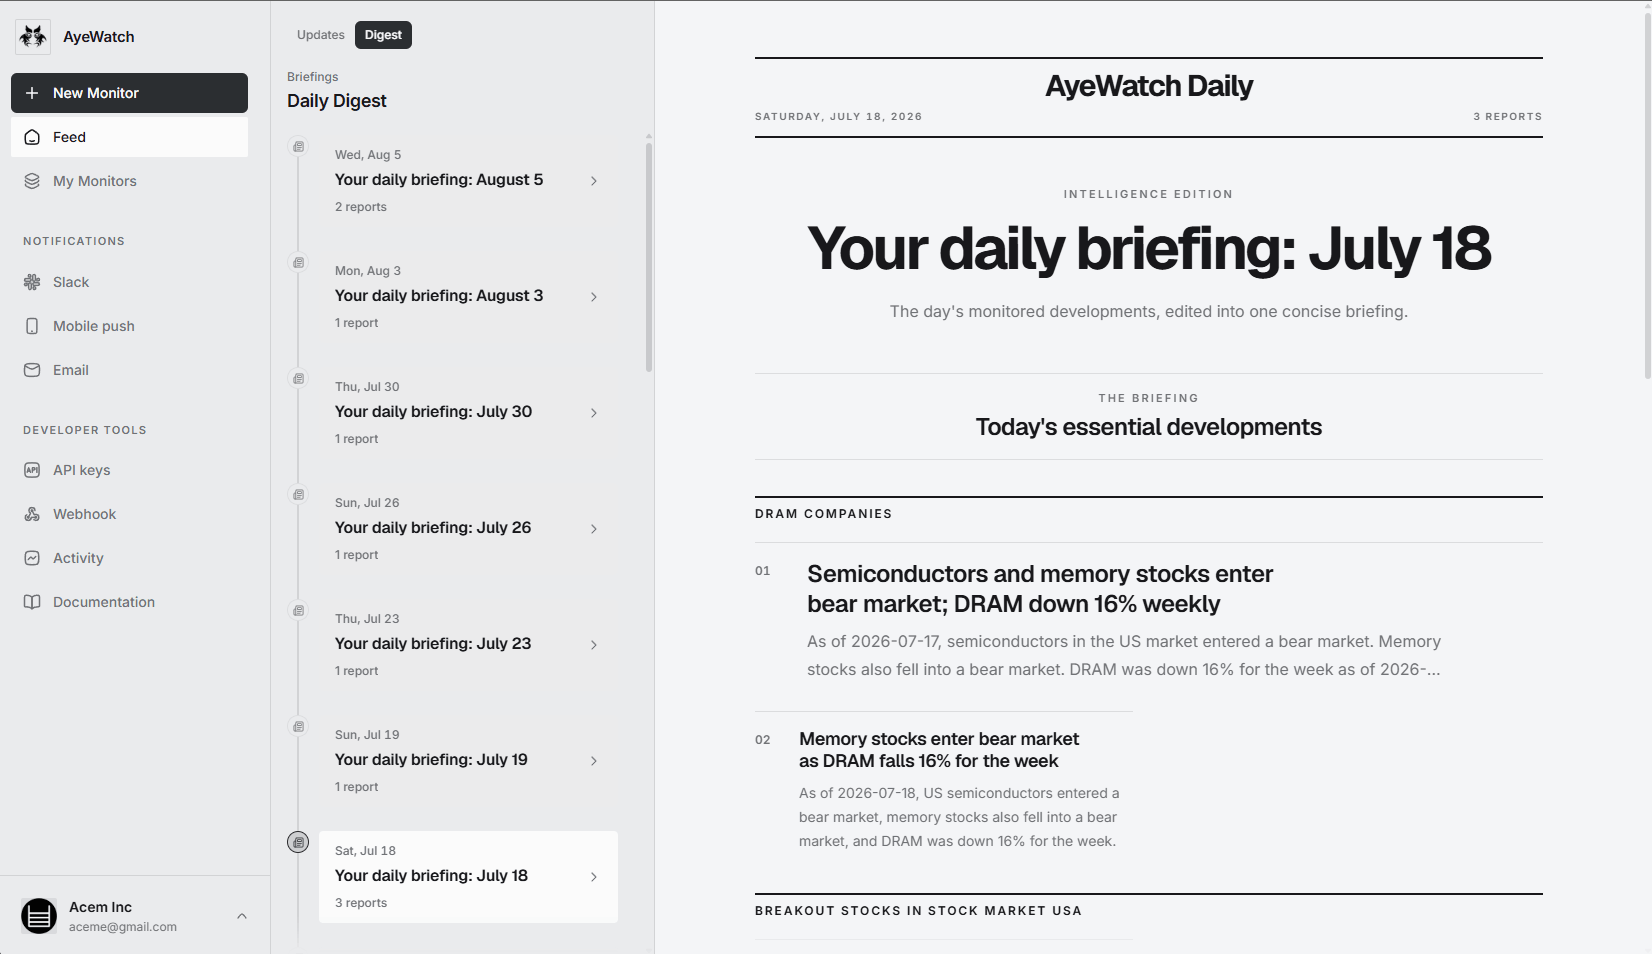
01 / 05Your update feed
Why security teams use Ayewatch
- Monitor every vendor in your stack for breach announcements and status-page incidents.
- Track CVE disclosures relevant to your tech stack.
- Monitor threat actor TTPs and ransomware leak sites.
- HMAC-signed webhooks pipe into your SIEM or ticketing system.
Topics security teams set up on day one
- ASAP mode
Breach announcements affecting cloud providers we use
Vendor-risk monitoring.
- 1 hour
New CVEs affecting Postgres or Node.js
Patch-readiness intel.
- ASAP mode
Status-page incidents for [Vendor]
URL monitoring on status pages.
The security teams workflow
- One topic per critical vendor + one per stack-component.
- Route ASAP topics to a #sec-alerts Slack channel and a webhook to your ticketing system.
FAQ
Is AyeWatch a CTI platform?
No, purpose-built CTI platforms (Recorded Future, Mandiant) go much deeper. AyeWatch is the lightweight open-source-intel layer for small security teams that want fast vendor + CVE alerting.
Do alerts come with severity scoring?
Alerts include AI summaries describing the nature of the event, but no formal CVSS-style scoring. Pair with a vuln scanner for prioritization.